How to set up AI automation on your VPS with a ChatGPT subscription
You can turn a Sentry error, a Linear ticket or a support chat into a pull request written by Codex, and pay for it with the ChatGPT plan you already have instead of API tokens. You need a VPS with 512 MB of RAM, a private GitHub repository and a few tokens copied from the tools you use.
This guide sets it up with automation-server, our self-hosted server that sits between your tools and Codex. Nothing gets merged or sent to a customer by itself: every result is an issue, a pull request, a private note or a Slack message that a person reviews.
- What you get
- How the pieces fit
- What you need
- 1. Deploy the server on your VPS
- 2. Open the admin
- 3. Connect GitHub
- 4. Run Codex on your ChatGPT plan
- 5. Install the workflows
- 6. Connect Sentry, Linear, Crisp and PostHog
- 7. Check that it works
- Know the limits before you rely on it
What you get
| When this happens | The server does | You get |
|---|---|---|
| A new error shows up in Sentry | Opens a GitHub issue with the stack trace and breadcrumbs, then Codex writes a fix with a regression test | A draft pull request |
| Someone adds the label codex to a Linear task | Starts a Codex run that implements the task | A pull request attached to the Linear task |
| Support tags a Crisp chat with triage | Asks an AI model whether it's a bug, a feature request, a question or spam | A private note in Crisp, and for a bug an issue or a draft fix |
| Monday comes | Pulls last week's numbers from PostHog | A report in Slack |
| You push to production | Codex reads the commits | A pull request with a changelog note |
You don't write code for any of it. You deploy the server, paste tokens into its admin and the automations switch on.
How the pieces fit
The work happens in 2 places:
- Your VPS runs the server and its admin. The server listens for webhooks from Sentry, Linear and Crisp, checks their signatures, skips duplicates and logs every run.
- GitHub Actions runs Codex. When an event needs a code change, the server starts a workflow in your repository. Codex reads the repo, makes the change and runs your checks. A later step in the workflow pushes a branch and opens the pull request.
Codex never gets a GitHub token. The push step that runs after it refuses to touch
.github/ or .agents/, so the agent can't rewrite its own workflow.What you need
- A fresh Ubuntu or Debian VPS. 512 MB of RAM is enough with the prebuilt image (the stack idles around 80 MB). Building the image on the server needs about 1 GB.
- 2 DNS A records pointing at it: one for webhooks (
hooks.example.com), one for the admin (admin.example.com).
- A private GitHub repository that will receive the pull requests. The Codex workflows refuse to run in a public one.
- A ChatGPT plan and the Codex CLI on your laptop.
- Accounts in the tools you want to connect: Sentry, Linear, Crisp, PostHog with Slack. Crisp triage also needs an OpenRouter key.
1. Deploy the server on your VPS
SSH into the VPS and run:
Terminal
Loading editor...
curl -fsSL https://raw.githubusercontent.com/prlct/automation-server/main/scripts/deploy-vps.sh | sudo bash
The script:
- installs Docker if it's missing and clones the repository to
/opt/automation-server
- asks whether to pull the prebuilt image (fast, 512 MB) or build on the server (1 GB)
- asks for your 2 domains and an email for Let's Encrypt
- asks for a GitHub repository, a GitHub token and a Sentry secret. Press Enter to skip them: you'll set them in the admin later
- generates the admin password and the secrets into
.envwith mode 600
- opens ports 80 and 443 if
ufwis on, and starts everything behind Traefik with HTTPS
At the end it prints the admin URL, the admin password and the webhook URL. Save the password in your password manager.
To update later, run it again. It pulls the new image and restarts, and keeps your
.env:Terminal
Loading editor...
sudo /opt/automation-server/scripts/deploy-vps.sh
💡
Something broke after an update? Set
IMAGE_TAG=sha- in .env to pin the previous build and run the script again. Set it back to latest to follow main.Traefik only exposes
/webhooks/* and /health on the webhook domain. Everything else there answers 404, including the admin's API.2. Open the admin
Open the admin URL and sign in with the email and password from the script. The admin is the only screen you'll use from here on.
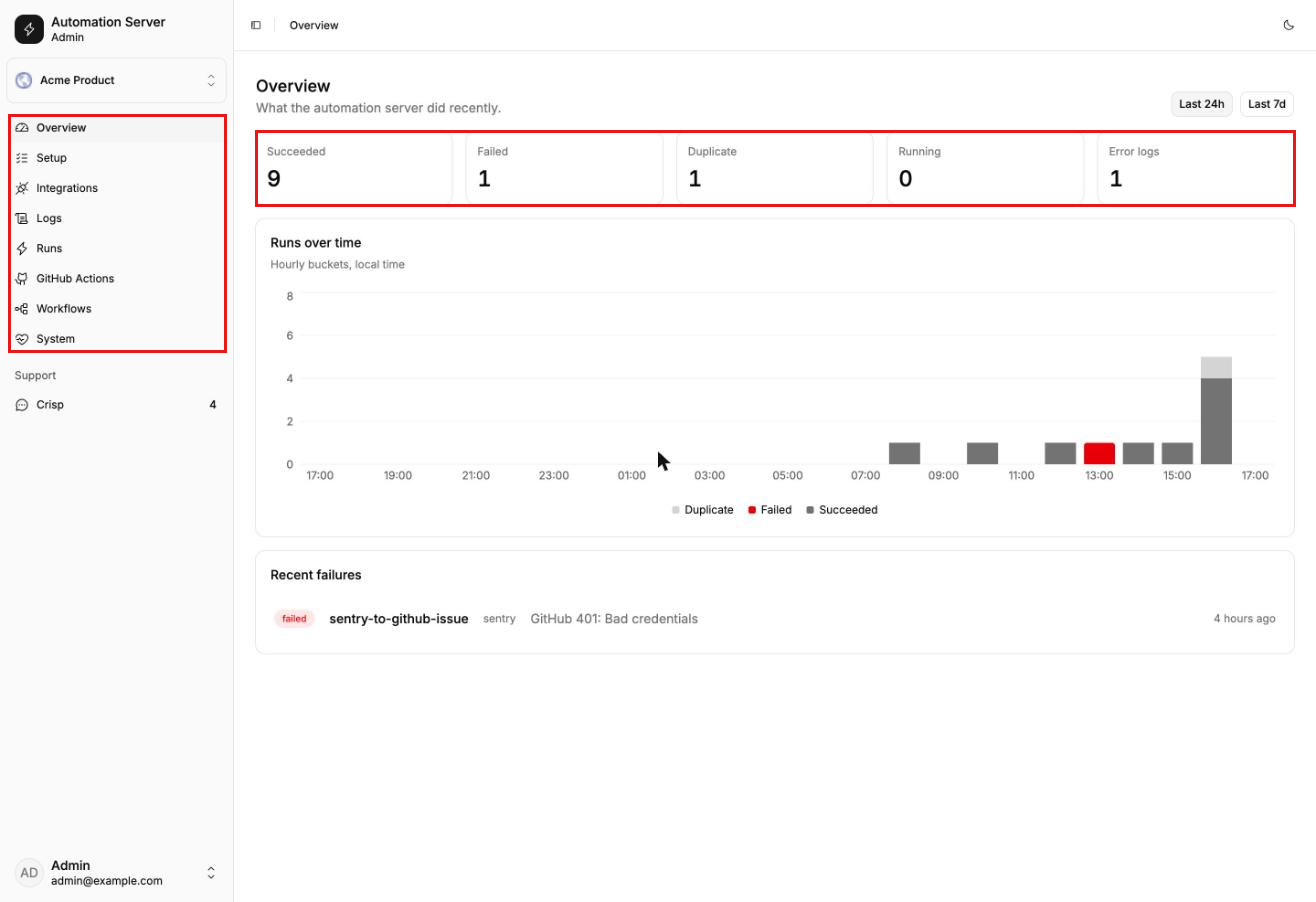
3 pages matter for setup:
- Setup is a checklist: GitHub token, repositories, services, workflows. It ticks each step as you finish it.
- Integrations has 1 card per service. Every token from this guide goes there.
- Workflows installs the Codex workflows into your repository.
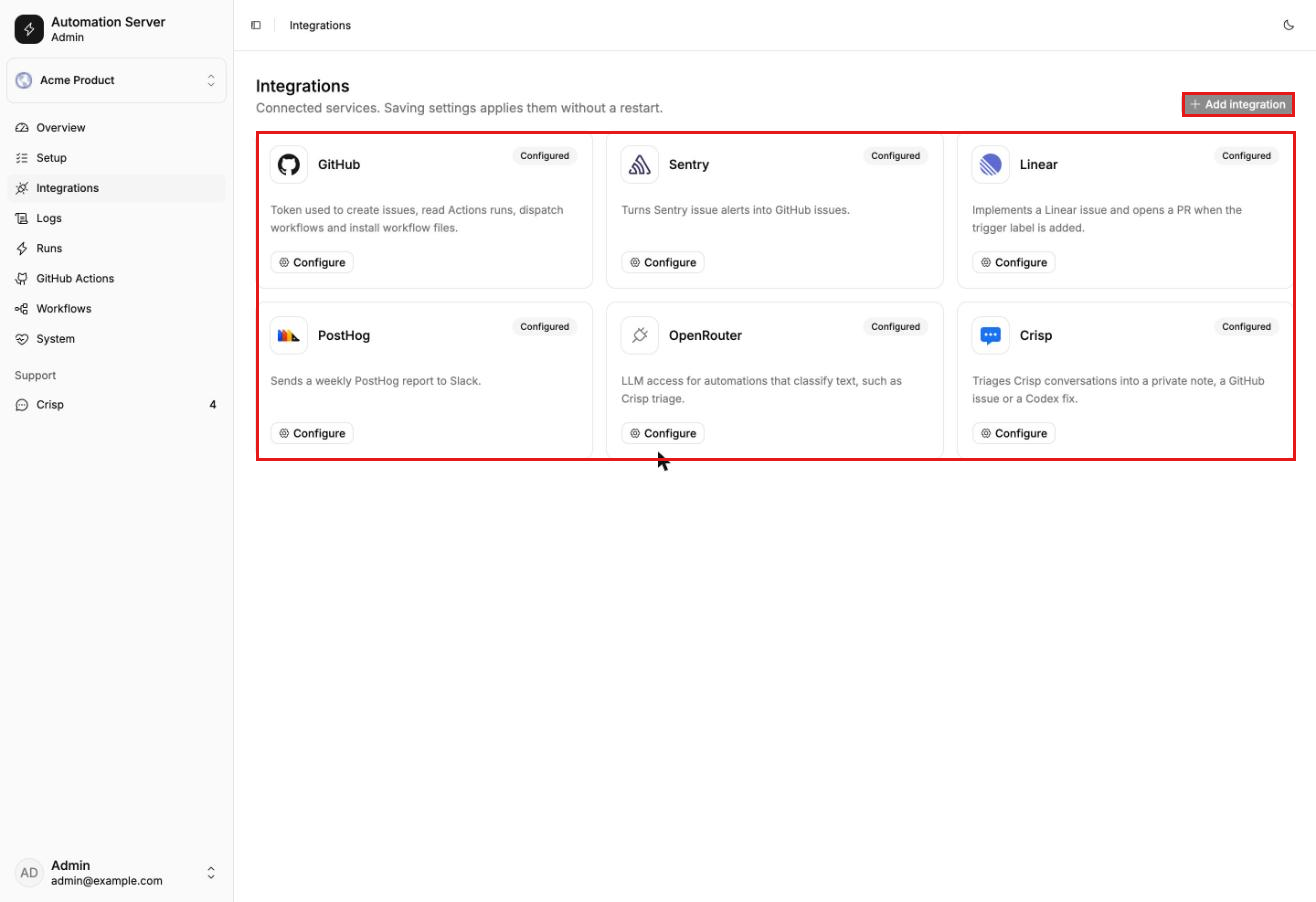
Every form works the same way. Paste a value, click Save, click Test connection. Saving applies at once, no restart. A saved secret shows Set and is never displayed again, and it's stored encrypted.
3. Connect GitHub
GitHub is shared by every automation, so it goes first.
Create a fine-grained token. Open github.com/settings/personal-access-tokens/new, pick only your target repository and give it these permissions:
| Permission | Access | Why |
|---|---|---|
| Issues | Read and write | Sentry and Crisp create issues |
| Actions | Read and write | Linear and Crisp start workflows, the admin shows runs |
| Contents | Read and write | The admin installs workflow files |
| Pull requests | Read and write | Installing in pull request mode opens a PR |
| Workflows | Read and write | GitHub requires it for any change in .github/workflows/ |
Write down the expiration date and put a reminder in your calendar. When the token expires, the server stops working with GitHub.
Save it in the admin. Open Integrations → GitHub, paste the token, set Issues repository to
owner/name and click Test connection.Let Actions open pull requests. In the repository, open Settings → Actions → General → Workflow permissions. Choose Read and write permissions, tick Allow GitHub Actions to create and approve pull requests and save. If the box is greyed out, an organization owner has to allow it first.
4. Run Codex on your ChatGPT plan
This is the step that makes Codex run on your subscription. The workflows log in with the same file the Codex CLI uses on your laptop.
- On your laptop, run
codex loginand finish the login in the browser. This writes~/.codex/auth.json.
- Open your repository, then Settings → Secrets and variables → Actions → New repository secret.
- Name it
CODEX_AUTH_JSONand paste the whole file. On a Mac,pbcopy < ~/.codex/auth.jsoncopies it.
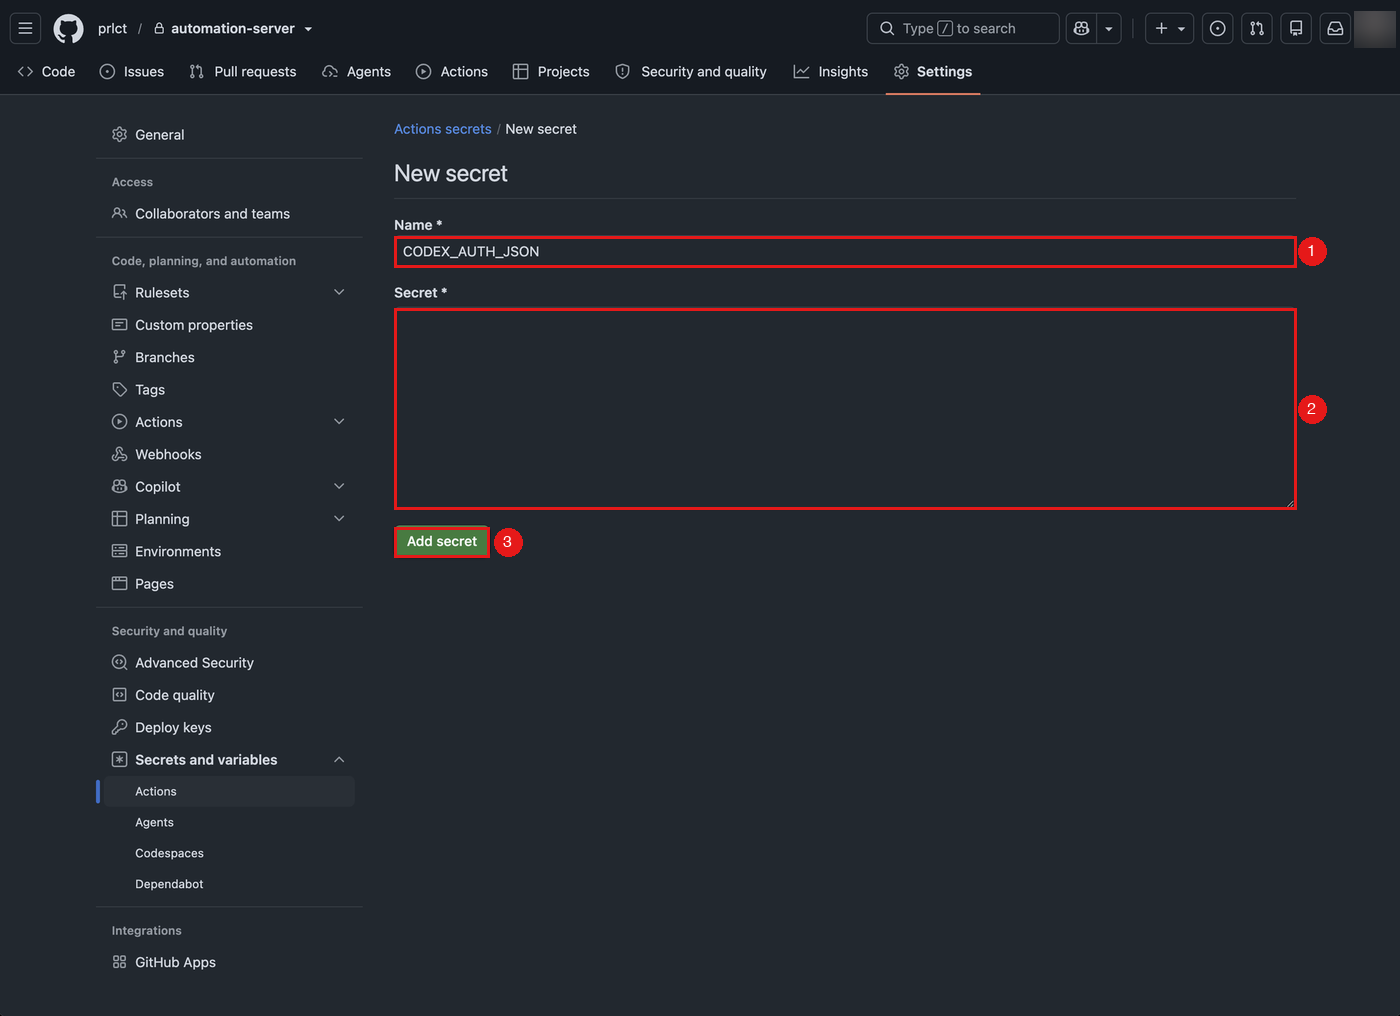
The login token inside that file changes every time Codex runs. Without help, the secret goes stale and the next run can fail. Add a second secret,
GH_PAT_FOR_SECRET_WRITE: a fine-grained token with Secrets: Read and write on this repository. The workflow then saves the new login back after each run.3 rules come with this secret:
- Private repositories only. The workflow stops with an error in a public one.
- 1 Codex run at a time. All workflows share 1 queue, because 2 runs in parallel would each rotate the same login.
- Never paste
auth.jsoninto an issue, a pull request or a screenshot. The workflow also refuses to open a PR whose text contains a value from it.
⚙️
Set the repository variable
CODEX_REASONING_EFFORT to high or leave it unset (the default is high). Without an explicit effort, Codex can run with reasoning turned off. CODEX_MODEL picks the model.The changelog and SEO workflows also accept an
OPENAI_API_KEY instead, which works in public repositories too. The issue fix and Linear workflows need CODEX_AUTH_JSON.5. Install the workflows
Open Workflows in the admin, pick your repository and choose how to install: Pull request opens a PR with the files, Direct commit writes to the default branch.
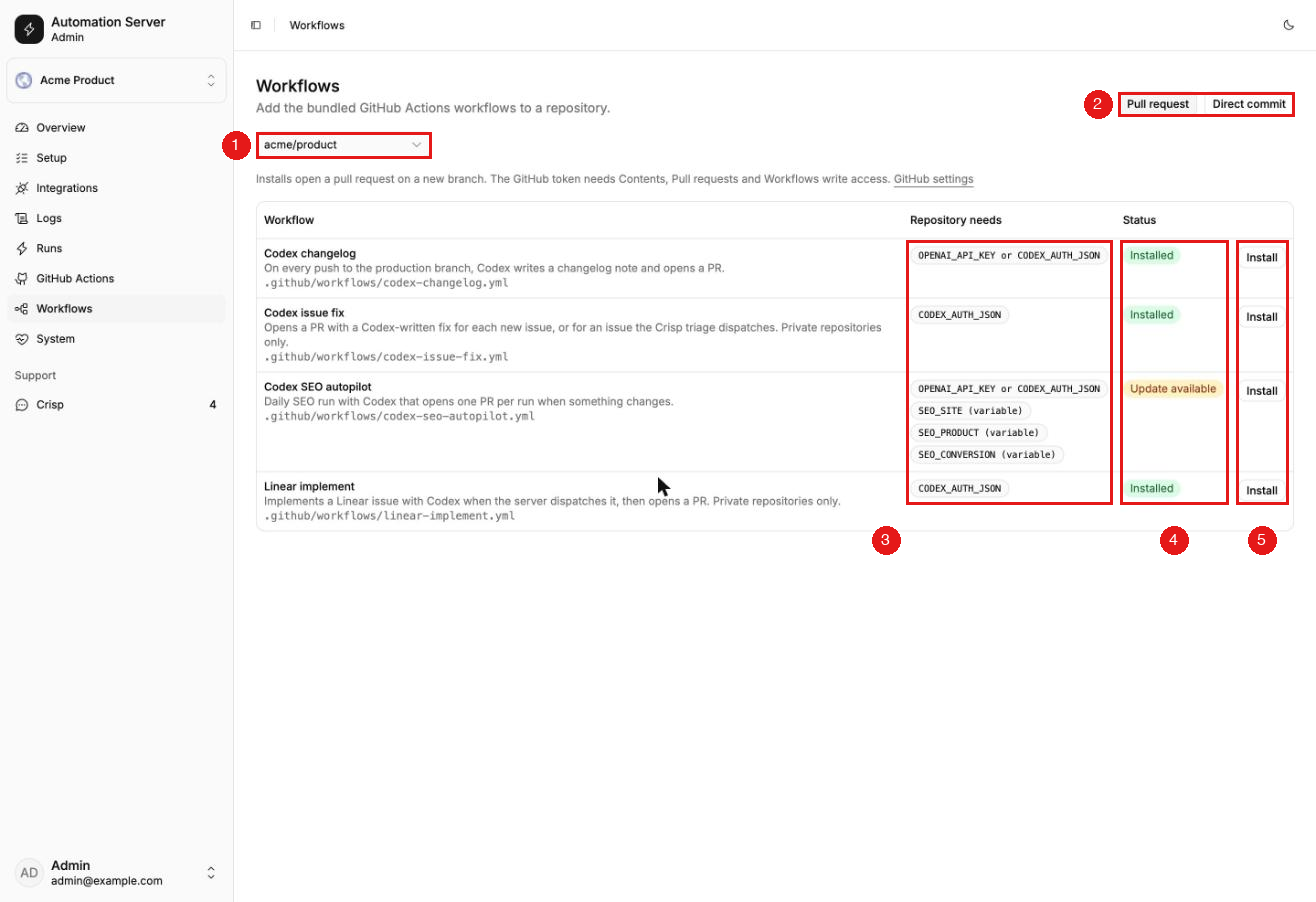
| Workflow | Starts when | You get |
|---|---|---|
codex-issue-fix.yml | A team member opens an issue, or the server starts it for a Sentry or Crisp issue | A draft PR with a fix and a regression test |
linear-implement.yml | The server sees the trigger label on a Linear task | A PR ready for review, attached to the task |
codex-changelog.yml | A push to your production branch | A PR with a changelog note |
codex-seo-autopilot.yml | Every day at 06:00 UTC | A PR with SEO fixes for your site |
Each workflow comes with a skill, a short instruction file in
.agents/skills/ that tells Codex how to do the job. The same Install button adds it. In pull request mode, merge the PR the admin opened: GitHub only runs a workflow once it's on the branch it starts from.Open the skill before the first run.
fix-issue came from another project and names that project's check commands (npx tsc --noEmit, npx vitest run, npm run lint). Swap in your own, or Codex will run the wrong checks.6. Connect Sentry, Linear, Crisp and PostHog
Connect only what you use. Each one comes down to the same 3 moves: copy the webhook URL from the admin, paste it into the tool, paste the tool's secret back into the admin.
Turn Sentry errors into fixes
- In Sentry, open Settings → Developer Settings and create an internal integration.
- Paste the webhook URL from Integrations → Sentry in the admin and turn on Alert Action.
- Save, copy the Client Secret and paste it into the admin.
- Create an issue alert with the trigger A new issue is created and the action Send a notification via your integration.
- Click Send Test Notification. A GitHub issue labelled
sentryappears.
By default only
error and fatal events become issues. Set SENTRY_ENVIRONMENTS=production to skip staging noise. A repeat alert for the same Sentry issue doesn't open a second GitHub issue.Hand Linear tasks to Codex with 1 label
- In Linear, create a label, for example
codex.
- Open Settings → API, add a webhook with the URL from the admin and keep only Issues checked.
- Copy the signing secret into Integrations → Linear, along with the label name and the repository that gets the PRs.
- Connect Linear's GitHub integration, so the PR shows up on the task.
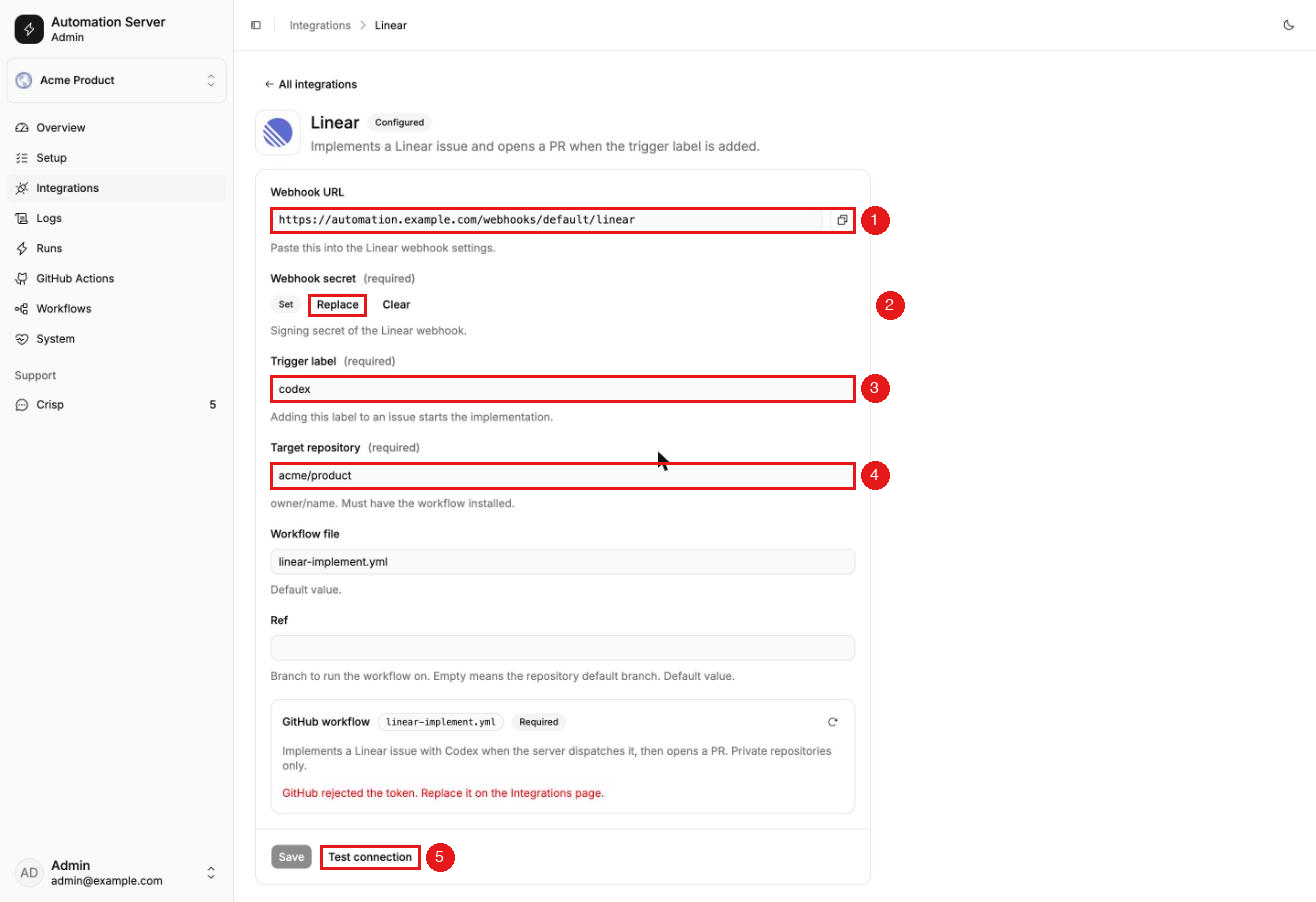
Add the label to a small, clearly written task. The PR title starts with the task ID (
ENG-42: ...), so Linear attaches it. Running it again for the same task updates the same PR.Sort support chats with Claude
Crisp triage is where Claude does the work. The server asks a model through OpenRouter to classify each chat it's asked about: Claude Haiku for the first pass, Claude Sonnet for bugs and unsure verdicts. Any model with structured outputs works.
Create an OpenRouter key with a credit limit and paste it into Integrations → OpenRouter. A classification costs a fraction of a cent, so a $5 limit covers a test and a small team. This part is pay per use, not your subscription.
Then add a Crisp plugin and its Web Hooks, and create a
triage segment. Start in shadow mode, which only writes a private note with the verdict. Switch to issue to open GitHub issues for bugs, or fix to start Codex on them too. A free Crisp plan can't receive private notes over the API, so use issue mode there. Personal data is stripped before the model sees the chat, and the customer never gets a message from the server.Get PostHog numbers in Slack every week
Paste a PostHog project ID, a personal API key and a Slack webhook URL into Integrations → PostHog. Pick a day and an hour. Use Preview report to see it before the first Monday.
7. Check that it works
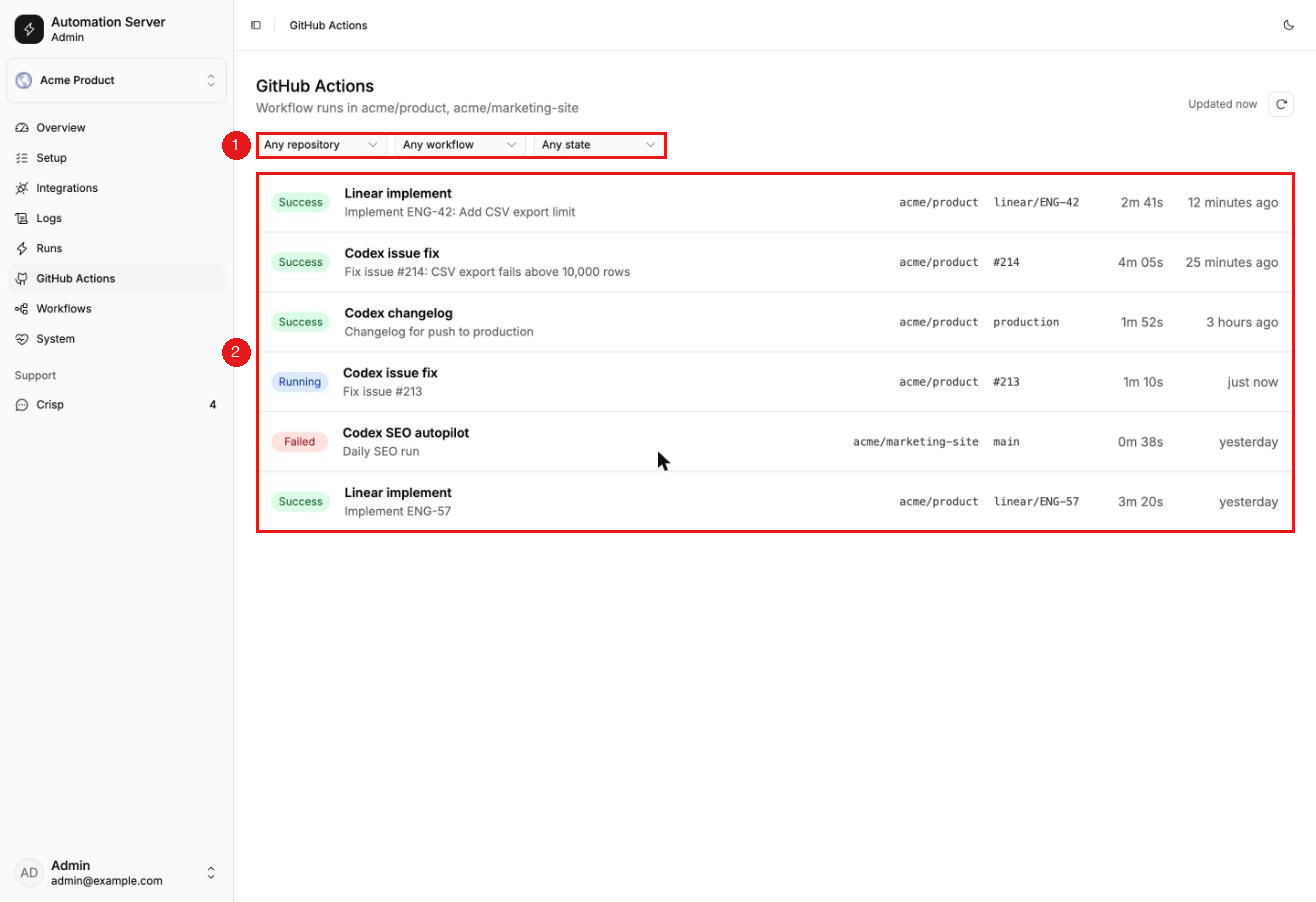
Run 1 real event through each automation, then look in 3 places:
- Runs in the admin: one row per automation that reacted to an event, with its result.
- GitHub Actions in the admin: every Codex run with its status, target and duration.
- Overview: counters for successes, failures and duplicates, and the latest failures. Open it first when something seems off.
| You see | Fix |
|---|---|
401 or 403 from GitHub | The token lacks a permission from step 3, or it expired |
404 when starting a workflow | The workflow isn't merged into the branch yet, or the token can't see the repo |
| The run fails on gh pr create | Actions aren't allowed to create pull requests yet |
CODEX_AUTH_JSON is not set | The secret is missing or sits in another repository |
| Sentry webhook rejected | The client secret in the admin doesn't match the integration. Copy it again |
Know the limits before you rely on it
- PRs opened by a workflow don't start your CI. GitHub doesn't trigger workflows from the job token. Push an empty commit or reopen the PR, or switch the push step to a GitHub App or PAT token.
- Some workflows haven't run end to end yet. The docs say so for the Linear, changelog and SEO workflows. Watch the first run of each.
- Keep tasks small. Codex makes no change when a Linear task is too vague, and says what's missing. Write the task the way you'd write it for a new hire.
- Keep
SETTINGS_ENCRYPTION_KEYstable. Change it and every secret saved in the admin becomes unreadable.
- Use a VPS, not a platform without a disk. On DigitalOcean App Platform the run history and duplicate checks reset on every deploy.
The full setup guides, with a screenshot for every click, are in the automation-server docs.
Ship faster than
your competition
Focus on customers and sales while we handle product delivery. Hire a dedicated AI maker or a whole product team.
Launch new products
Fix your delivery
Hit fundraising milestones
[Analytics Chart]
Wireframe v0.1
Sarah Chen CEO, Founder
$127k
MRR
2,847
Customers
+23%
Growth
Sales Performance
Latest Deal
Enterprise plan closed
Acme Corp · $12k/mo


Services
Industries
Hire
Claude Code Devs Next.js DevsReact DevsReact Native DevsSupabase DevsLovable DevsAI EngineersFull-stack Devs Upwork Alternative
AI Tools
Resources
Kickstart No-Code Stack Tech Stack Tech Trends AI SaaS Skills MCP Servers Academy Help Center Blog Changelog
Our products


© 2026 Paralect, Inc 651 N Broad St, Suite 206, Middletown, 19709, Delaware, United States